
You can feel the mess before you can name it. A freelancer finishes a client site in Elementor, hands over the dashboard, then three months later gets a new login request from the same client, a contractor, and a marketing assistant who nobody remembers adding. On another site, WooCommerce customers, staff, and a third-party support rep all end up inside the same admin area, and every password reset becomes a small incident.
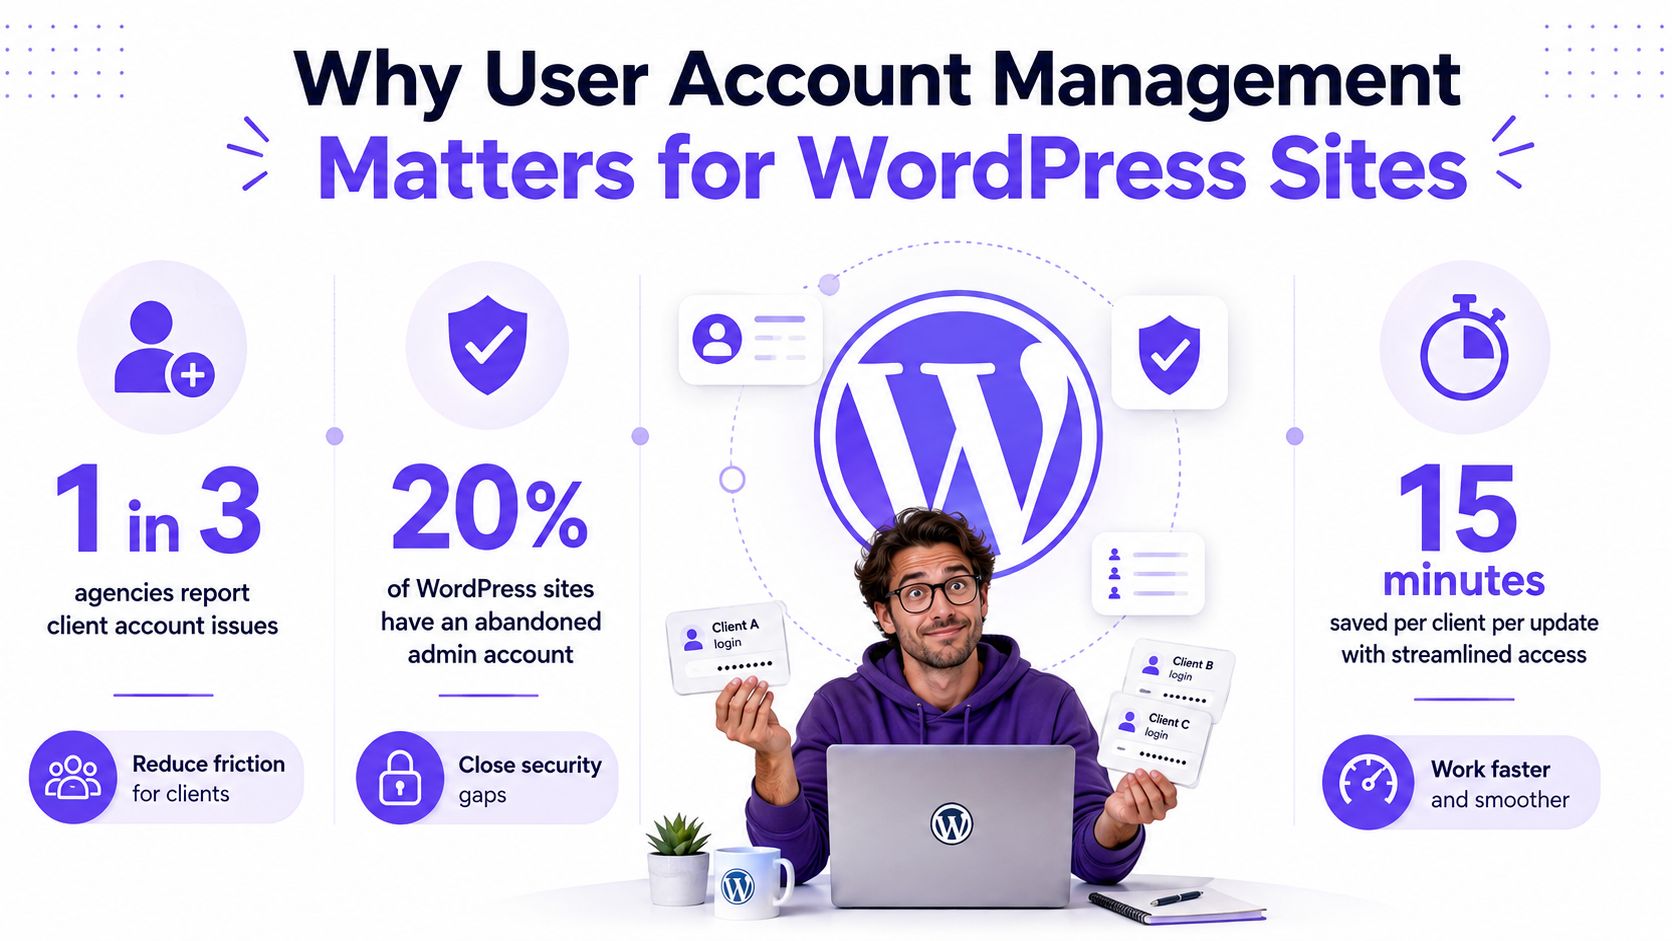
That's the shape of user account management on WordPress sites. It's not a settings-page chore, it's an identity lifecycle problem, and the scale of that problem is bigger than most site owners think. One 2025 industry analysis estimated that organizations now manage more than 300 billion passwords worldwide, while another projected over 423 billion passwords in use globally, based on 5.64 billion users with about 75 passwords each; the same analysis said the average number of passwords per person rose from about 100 in 2020 to more than 250, and that almost 24 billion usernames and passwords were reported compromised in 2022 alone, all of which points to account management as a constant control problem, not a one-time setup task (password statistics analysis).
Why User Account Management Matters for WordPress Sites
A typical agency site shows the problem fast. One designer owns the staging logins, the client has three editors, a freelancer comes and goes, and the WooCommerce store manager wants access to orders without seeing everything else. None of that is unusual, but it becomes a tangle when the site grows through launches, revisions, and one-off exceptions.
The hidden cost is not just security
Most WordPress teams feel account management as friction before they feel it as risk. People reuse credentials because new accounts are slow to provision, support tickets pile up because old logins never got removed, and every abandoned account becomes another thing to audit when something looks off. The operational pain is real because modern sites rarely have one neat identity boundary.
Practical rule: if you can't answer who owns an account, why it exists, and when it should disappear, the account is already a liability.
That's why the industry numbers matter. The scale of passwords and username exposure shows that account sprawl is normal now, not exceptional, and a WordPress site sits inside that wider environment whether the owner thinks about it or not. When a contractor leaves, an old staging user remains active, or a temporary support login sticks around after launch, the issue isn't the login form. It's the lack of lifecycle discipline around creation, access, review, and removal.
WordPress sites feel the problem in daily work
The practical symptoms are easy to spot. A client can't remember which email was used for registration. A marketing assistant has the right access on the live site but not on staging. A shop manager needs limited dashboard access, but the only way anyone knows to do that is by making them an editor and hoping for the best. None of those are platform failures, they're account-lifecycle failures.
That's the mindset shift. User account management is the discipline of making sure every account has a purpose, a scope, and an end date. In WordPress and Elementor, that means building a process that covers onboarding, access changes, and offboarding without turning every request into a manual exception. Once you treat it that way, the rest of the site gets easier to run.
What User Account Management Actually Means
At a practical level, account management is the same idea as handing someone a passport, a badge, and a job description, then taking those things back when they no longer belong. The account is the identity, the role is the job, and the expiry or revocation is the offboarding step. If any one of those is missing, the system is incomplete.
It's broader than login screens
A lot of WordPress content uses account management as a synonym for authentication, membership, or registration forms. Those are only pieces of the system. Authentication answers who someone is, authorization answers what they can do, and lifecycle management answers when access starts, changes, and ends.
That distinction matters in real projects. A login form can work perfectly while the underlying access model is a mess. A membership plugin can collect profiles cleanly while stale contractor accounts still have admin rights. A polished registration page doesn't help if nobody reviews who still has access after the project closes.
For a useful mental model of how identity handling breaks into separate controls, the AAA breakdown in AAA with Cisco Meraki explained is worth a look. The point isn't the branding, it's the structure, because WordPress teams tend to conflate the three and then wonder why access problems keep coming back.
In WordPress, every part is part of the same system
A clean WordPress setup touches the login form, the profile page, role assignment, session handling, and deprovisioning. Elementor changes the experience layer, not the underlying identity logic, so the builder has to be matched with the right account rules. If the user can register on the front end but never gets reviewed later, the site has a welcome flow, not account management.
This is also where operational thinking helps. The best setups don't just ask, “Can the user log in?” They ask, “Should this user exist, what can they touch, and who signs off when that changes?” That question is what separates a working site from an unmanaged one.
The Core Components Every Site Needs
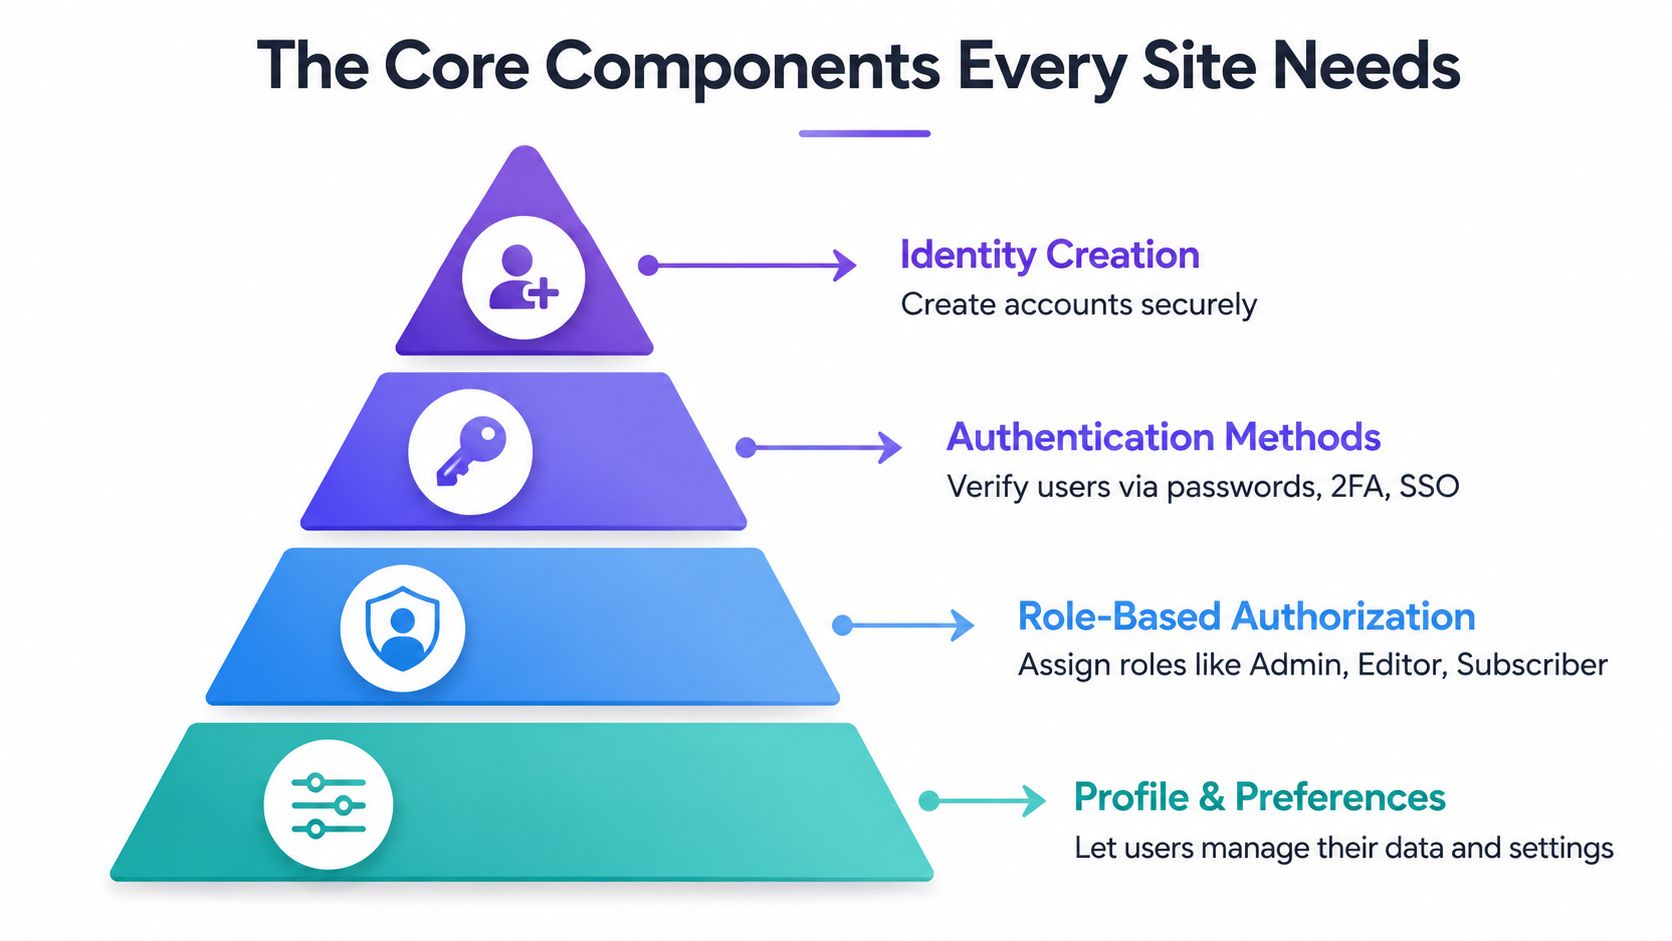
A real account system is easier to manage when you treat it as a lifecycle, not a settings page. Creation comes first, then authentication, then authorization, then profile management, and then audit plus account retirement. WordPress has primitives for all of these, but the platform only behaves well when the pieces are connected instead of treated as separate chores.
A contractor gets added for a launch, a client gets dashboard access for approvals, a volunteer software workflow needs limited permissions, and a forgotten admin account lingers after the project ends. Those are the failures that show up in live sites, especially on builds assembled with Elementor and membership plugins. For a practical example of how membership sites get assembled in WordPress, building membership websites with Exclusive Addons shows how the front end can be shaped without losing sight of the account model.
Identity, access, and behavior each need their own control
Identity creation is the record itself, usually anchored in wp_users and related metadata. That account should be created with a clear owner and purpose, not as a spare login “just in case.” Authentication is the gate, which is where passwords, two-factor methods, and session controls matter. Authorization is what the user can do, and in WordPress that's where roles and capabilities do the heavy lifting.
Profile and preference management live closer to wp_usermeta, where extra data, contact details, and display preferences tend to accumulate. That is useful, but it also means you need discipline about what belongs there. If profile data becomes a dumping ground for business logic, later reviews become painful, and account cleanup gets messy fast.
Least privilege means the account should do one job, not three.
If a user needs to edit posts, they should not automatically inherit shop settings, theme controls, or plugin access.
Logging and lifecycle rules keep the system honest
Audit logging answers who changed what and when. Lifecycle automation handles the point where accounts expire, get disabled, or get deleted. Enterprise guidance treats account inventories and recurring authorization reviews as standard practice, with dormant accounts disabled or removed on a schedule where supported (NIST-aligned account management guidance). That logic fits WordPress too, because the risks are the same even if the stack is smaller.
The order matters. If creation is easy but offboarding is manual, the site drifts. If roles are broad but profiles are tidy, the wrong people still have access. If logging exists but nobody reviews it, you are only storing evidence after the fact.
The practical takeaway is simple. Design the system from top to bottom, not from the login form outward. WordPress gives you the parts, but lifecycle discipline decides whether the parts hold together.
Setting Up Roles and Capabilities in WordPress
Default roles are useful because they're familiar, but they're not enough on their own for most client sites. The built-in model makes sense for a simple blog, then starts to creak when you have editors, shop staff, clients, contractors, and contributors all sharing the same dashboard. That's where custom roles and capability control earn their keep.
Use the built-in roles as a starting point, not a finish line
WordPress ships with a useful baseline, but the question is always what each person really needs. An Administrator can do almost anything, which makes it appropriate for site owners and technical leads, but dangerous as a default. An Editor can manage content, which works for editorial teams but not for clients who only need approvals. A Subscriber can usually just log in and manage their own profile, which is fine for membership areas but too limited for operational staff.
| Role | Typical Use | Key Capabilities | Risk If Overused |
|---|---|---|---|
| Administrator | Site owner, lead developer | Full site control | Broadest blast radius |
| Editor | Content manager | Publish and manage posts | Too much control for casual users |
| Author | Regular content creator | Publish and manage own posts | Limited oversight if left unchecked |
| Contributor | Draft writer | Write drafts, no publishing | Friction if team needs review flow |
| Subscriber | Member or customer | Log in and manage profile | Not enough for staff tasks |
| Shop Manager | WooCommerce operations | Orders, products, store settings | Can be too broad for non-ops users |
Custom roles make client work saner
For agency builds, custom roles usually beat role abuse. If a client only needs to review submissions, a custom role with a few capabilities is cleaner than handing out editor access and hoping they don't wander into the wrong screen. If a store manager only needs order handling, a store-specific role keeps the dashboard narrower and easier to support.
A plugin like volunteer software is a good reminder of the same principle in another context. Even outside WordPress, access has to match duties, not job titles, and the structure of the role should reflect the workflow.
If you want a UI for role editing instead of custom code, User Role Editor is a common choice because it lets you adjust capabilities without rewriting membership logic. For Elementor teams, the useful pattern is to gate dashboard sections by capability, not by hiding links and hoping users don't discover the page. Exclusive Addons' User Permission Management feature fits that style of setup when you want role-aware layouts without building your own conditions from scratch.
Use permissions with intent
The rule is simple. Give users just enough access to do their job, and no more. If a role needs to expand temporarily, make that change visible and reversible, not permanent by accident. That approach keeps the site easier to operate and much easier to audit later.
Designing Login, Registration, and Profile Flows in Elementor
The best Elementor account flows feel like part of the site, not a plugin bolted onto the side. That matters because users judge trust by the quality of the first interaction, and staff judge the system by how many steps they need just to get in and finish one task. A clean front-end flow reduces support work and makes offboarding easier later because the same structure can be used for account changes too.
Build the flow around people, not around forms
A good client portal usually has three paths. The designer logs in to upload assets, the client reviewer logs in to approve work, and the project manager logs in to track progress. Each one should land on a dashboard that matches their role, not on the same generic admin page with half the menu hidden.
That's where Elementor helps if you're disciplined. Use a custom login page, a clear registration form, and a profile editor that only exposes fields the user should touch. Exclusive Addons' login page WordPress resources fit naturally into that pattern when you're assembling a front-end entry flow rather than sending people to /wp-admin.
Small UX details do a lot of work
Inline validation keeps people from submitting broken emails or weak passwords. A visible password-strength meter helps users finish registration without support intervention. Confirmation states after signup matter because they tell people the account was created and what happens next, instead of leaving them wondering whether the form disappeared into a void.
Social login can reduce friction, but only where it fits the audience. For a member community or a low-friction customer area, it can help. For a client portal with sensitive files, I'd rather see a deliberate sign-in process and a clear password-reset path than a convenience shortcut that nobody reviews later.
Conditional access keeps the dashboard tidy
When a client, reviewer, and staff member all use the same portal, the dashboard should adapt by role. Show project cards, billing details, or submission status based on permission, not on the hope that users won't click around. Exclusive Addons can help here because its conditional visibility and templates make it easier to build those states visually instead of hard-coding every variation into a theme.
A practical offboarding flow should work in reverse too. If a contractor leaves, the account should stop seeing project widgets immediately, and the profile page should no longer expose edit paths or private records. That way, registration, login, profile editing, and revocation all sit inside one predictable system.
The Hidden Risk of Forgotten and Shared Accounts
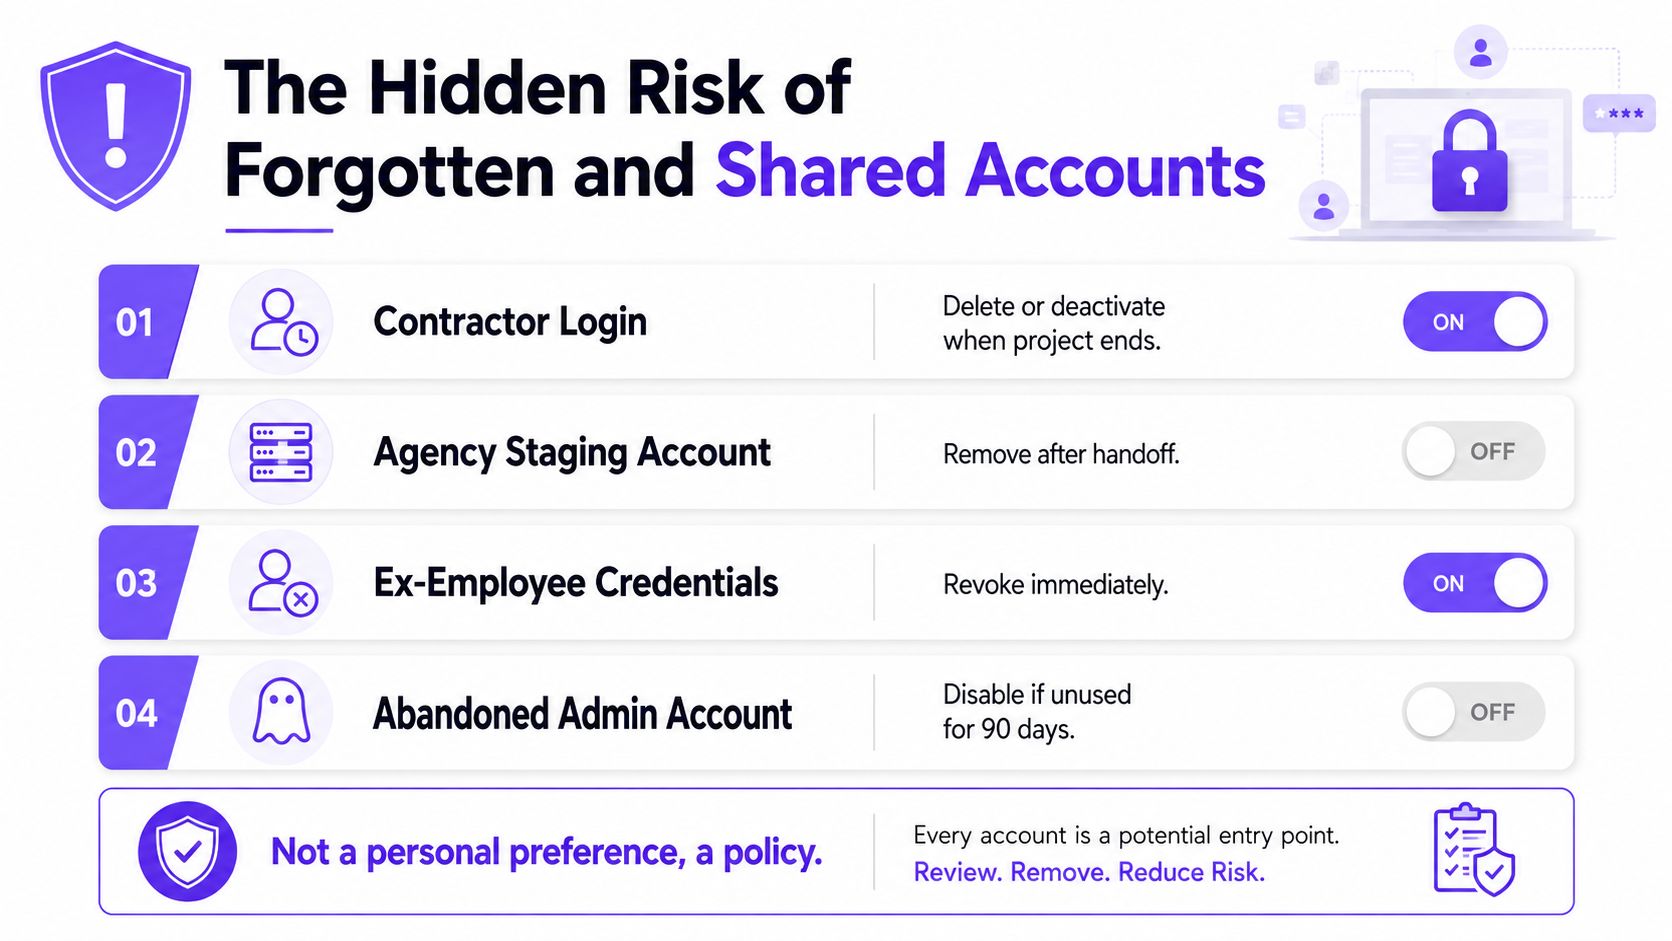
Most account-management guides spend too much time on passwords and too little time on the accounts nobody remembers. That's a gap. Forgotten contractor logins, shared social media accounts, staging users, and default admin accounts from early setup can linger long after the work is finished, and they're exactly the kinds of accounts that create quiet access risk.
The accounts that survive the project are the problem
A contractor gets access for one sprint, then the sprint ends and the login stays active. An agency creates a staging admin for testing, then hands over the site and never removes it. A social team shares one mailbox-linked login because it's faster than creating individual accounts. None of those choices feels catastrophic in the moment, but they blur ownership and make cleanup harder later.
Independent security guidance warns that forgotten accounts are often overlooked, shared accounts make ownership unclear, and temporary accounts should have expiry dates. MITRE's account-management mitigation also recommends keeping an inventory of all accounts and validating active accounts on a recurring schedule at least quarterly (forgotten accounts risk guidance). That lines up with enterprise controls that require inventories, periodic review, and central account administration.
WordPress teams need a cleanup rhythm
For WordPress, the workflow doesn't need to be fancy. Run scheduled user reports, review roles against real responsibilities, and put expiry rules around temporary accounts. If a project is over, the account should be disabled or deleted, not just “left there for now.” If a person changes teams, their access should be modified instead of duplicated.
Shared access feels efficient until nobody knows who did what.
That's why the hidden risk isn't the login screen, it's account sprawl. A site can look tidy from the outside and still have stale users, overbroad roles, and orphaned staging access sitting underneath. The fix is boring but effective. Keep an inventory, review it regularly, and treat every extra login as something that needs an owner and an end date.
Offboarding should be a workflow, not a favor
When someone leaves, the account exit should happen the same way every time. Disable access, remove unused privileges, and document the change. That makes the site easier to support and a lot easier to audit when something goes wrong.
Security, Analytics, and an Operating Rhythm That Sticks
A WordPress site can have good controls on paper and still drift into sloppy access if nobody watches the pattern over time. Two-factor authentication, brute-force protection, and login activity logging all help, but they only matter when someone checks the results and responds. The same applies to account analytics. Active users, failed logins, and role distribution show whether the access model still matches how the site is used.
Track a few signals and act on them
If failed logins spike, someone may be guessing passwords or users may be struggling with the flow. If dormant accounts keep appearing, offboarding is slipping. If role distribution keeps drifting toward too many administrators, the site has lost discipline. Those signals do not need a giant dashboard. They need a regular review habit.
If you want a security-focused reference point for comparing plugin and platform choices, the security analysis of WebinOne is useful for understanding how teams think about access and safety in a broader site-management stack.
Keep the cadence light enough to maintain
Weekly reviews can stay short. Check recent logins, confirm that temporary users still need access, and look for any account that should have expired already. Monthly, review broader role patterns and cleanup tasks. Quarterly, do the deeper authorization review that enterprise guidance expects. That is the point where privilege creep usually starts to show itself.
Here is a simple operating rhythm that holds up well:
- This week: enable 2FA for privileged accounts, review the newest contractor logins, and turn on login activity logging.
- This quarter: audit dormant accounts, check role assignments against current responsibilities, and disable anything temporary that never got closed out.
- This year: reassess the entire account lifecycle, from registration to offboarding, and remove any workflow that exists only because “that's how we've always done it.”
Make the process visible to the team
The goal is not compliance theater. It is a site that stays understandable after launch. When account controls, analytics, and user experience all point in the same direction, the site runs with less friction and fewer surprises. A practical setup also makes contractor access, staging accounts, and forgotten logins easier to spot before they turn into support work.
That is the point where WordPress account management stops feeling like cleanup and starts functioning like a real operational system.